Security and preventing hacks
Hi IH!
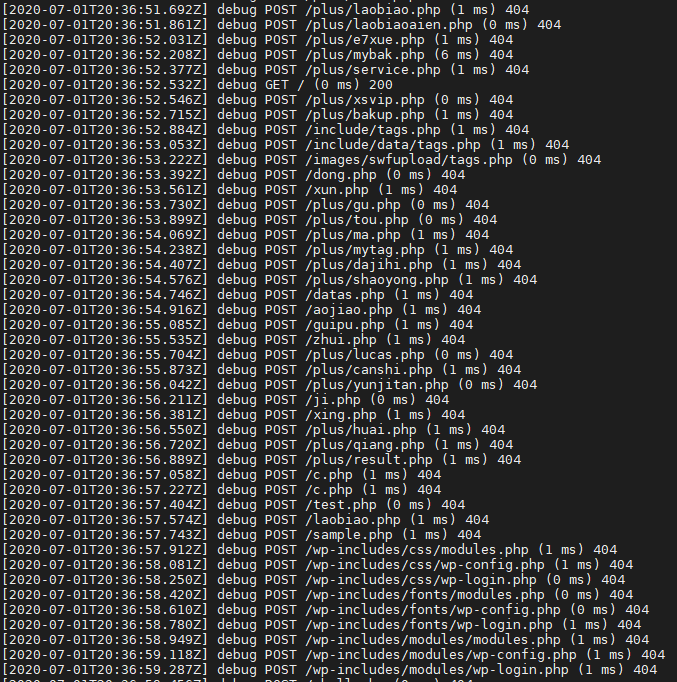
Today I had to investigate a weird bug in the project I'm building ( theLIFEBOARD ) so I went to my server and check the API logs to see if there was something weird and I found tons of weird things... As you can see in the image, my API was receiving tons of requests in a lot of endpoints which are not actually part of the API (even requests to /wp-login or /phpMyAdmin...), hence the 404 responses
I guess these are just random people trying to identify if I use WordPress, or any other common CMS, trying to find exploits and vulnerabilities... what can you do...
I'll try to investigate what is going on and what can I do to avoid any issues but I'm not an expert in the field and I know that as much as I do, there is always going to be a way to get hacked.
How do you usually approach security? What are the essential things that you always do? Have you ever been hacked? If so, what happened and what did you learn?
I hope we can share some knowledge and be safer out there.
Happy coding!

Hi Antonio, this is life on the Internet. What you have in your logs is bot activity and very common. Basically if a vulnerability is discovered in a common publishing platform like Wordpress or a web application framework (Django), it will get weaponized by malicious actors and they will just scan the IPv4 address and send out requests hoping it finds a server running stale software and they can own it.
You can prevent this by updating critical software in your application. If you use something like Django then stay up to date.
Sanitize all inputs in your web applications, check the format of inputs, values, boundaries, etc... before processing them.
Secure programming is a broad topic, check out the OWASP for more resources and advice:
https://owasp.org/www-project-top-ten/
If you have any specific questions let me know but OWASP will definitely help inform you quite a bit if this area is new to you.
Well, that isn’t totally surprising. What can you do? a lot but it entirely depends on your setup and architecture. I can suggest rate limiting your APIs or do an IP whitelisting. create a firewall there are tons of things you can do and you should do it.
Security shouldnt be an after thought
If your data is not secure, your privacy is at risk. Read more here https://celltrackingapps.com/couple-tracker/ on how partners can follow each other over the phone.