Automating SOC2 Compliance: How to Deploy a security.txt on the Cloudflare Edge
Hey everyone,
If you are currently building or scaling a bootstrapped B2B SaaS, you already know that security compliance audits (like SOC2, ISO 27001, or the EU's NIS2) are the ultimate gatekeepers to winning lucrative enterprise contracts [1].
One of the basic, global requirements under RFC 9116 is hosting an active vulnerability disclosure policy at /.well-known/security.txt so security researchers can safely report issues to your team.
But as bootstrapped founders, we face a major hosting bottleneck: many of our marketing websites, blogs, or landing pages are hosted on restricted static CMS platforms (like Webflow, Shopify, Wix, or Blogger) that completely block us from creating custom files inside the root /.well-known/ directory.
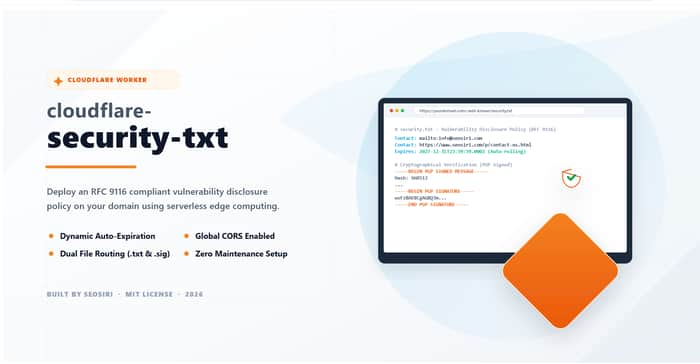
To solve this friction, I open-sourced cloudflare-security-txt—an enterprise-grade, serverless Cloudflare Worker template to deploy your security policy instantly at the edge!
Why this is a more robust, zero-maintenance template:
⚙️ Dynamic Auto-Expiration: Under RFC 9116, the Expires: date is strictly mandatory. To prevent your file from expiring and throwing critical warnings on automated corporate compliance scanners, this worker automatically calculates and rolls your expiration date exactly 1 year in the future dynamically.
🔐 Dual Route Serving: It natively supports serving both your raw security policy (/.well-known/security.txt) and its cryptographic PGP signature (/.well-known/security.txt.sig) for enterprise-grade audits.
🌐 Global CORS Enabled: Enforces wildcard CORS headers, allowing global security scanners and vulnerability crawlers to parse your files cleanly via AJAX/fetch requests.
We have successfully launched this template fully public on GitHub, and it is ready for 1-click deployment!
👉 Deploy with 1-Click on GitHub https://github.com/SEOSiri-Official/cloudflare-security-txt
👉 Read the Full GTM Implementation Playbook on SEOSiri https://www.seosiri.com/2026/07/deploy-rfc-security-txt-cloudflare-workers.html
I'd love to hear from other indie hackers here:
Are you currently hosting a certified security.txt on your production domains? How are you handling automated compliance audits and zero-maintenance file expiry in your bootstrapped setups? Let's trade notes!
