The "Anti-SaaS" Framework for WordPress Security — Built for Makers. 🛠️🚀
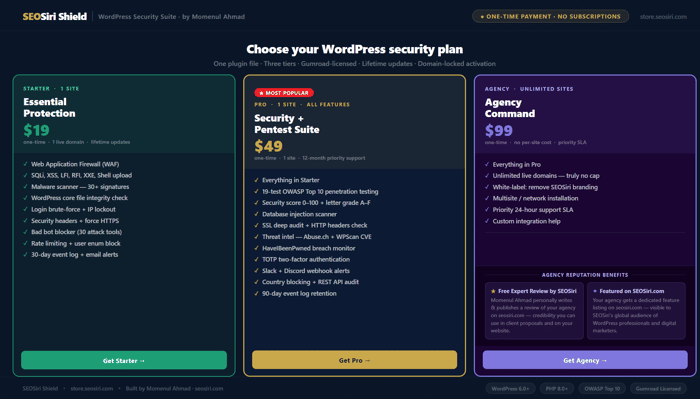
As developers, we’ve all fallen into the "Subscription Trap." A simple security plugin starts at $10/month, and suddenly your "lean" project has $120/year in technical overhead. If you're managing 10 sites, that’s $1,200/year just to keep the lights on.
I built the SEOSiri Shield to kill that overhead. It’s a professional-grade security engine built on a One-Time Payment model. You buy the code once; you own the protection forever.
Why developers will love the architecture:
Pre-Bootstrap WAF: Our firewall hooks into the early mu-plugins cycle, dropping malicious SQLi/XSS payloads before WordPress even initializes its heavy objects.
19-Test OWASP Pentest Engine: We’ve automated a deep-level security audit mapped to the OWASP Top 10 2021. It gives you a quantifiable 0–100 score—not a "check the box" feeling.
DevOps Integration: The Agency tier includes a full REST API and Slack/Discord Webhooks. Get real-time JSON payloads for critical events (core file changes, lockouts) directly in your dev channel.
Zero Bloat: No "marketing dashboard" junk. Just high-performance security hardening.
The $99 Agency Hack: For less than the cost of one year of a "Pro" subscription elsewhere, you get Unlimited Site Licensing. Use it on every project you ever build. No per-site fees. No recurring bills.
I’d love to get some technical feedback on our WAF logic from this group:
👉 Full Technical Briefing: https://www.seosiri.com/2026/04/wordpress-security-shield-guide.html
#BuildInPublic #DevOps #WebSecurity #WordPress #IndieHackers
