proworkbench
Local-first AI agent platform with approvals-first execution
Over the past year, AI agents have shifted from experiments to real operational systems. They can write software, control browsers, execute workflows, and increasingly make decisions on behalf of users.
But while most discussions focus on how autonomous agents can become, I kept running into a different question:
How do you safely run agents that can actually execute actions?
That question led me to build ProWorkBench.
Project: https://proworkbench.com
Code: https://github.com/jamiegrl100/proworkbench/
The Problem With Current Agent Architectures
Most modern agent systems optimize for maximum autonomy:
Give the model tools
Let it plan
Let it execute
Hope guardrails hold
This works well for demos. It becomes risky the moment agents interact with real systems.
Agents today can:
Hold credentials
Modify files
Run scripts
Trigger workflows
Interact with APIs
At that point, they are no longer assistants — they are operational actors.
We solved intelligence before we solved control.
Local‑First as a Design Constraint
Instead of starting from cloud autonomy, I started with a constraint:
Execution should stay on the user’s machine.
Local‑first architecture changes several things:
Users control their model endpoint
Workflows remain private
Failure domains are smaller
Infrastructure cost is predictable
ProWorkBench connects to:
Local LLM servers
External APIs (optional)
User‑controlled execution environments
The platform does not own your intelligence layer — it orchestrates it.
The Core Idea: Approvals‑First Execution
The main architectural decision was simple:
Agents should propose actions before executing sensitive operations.
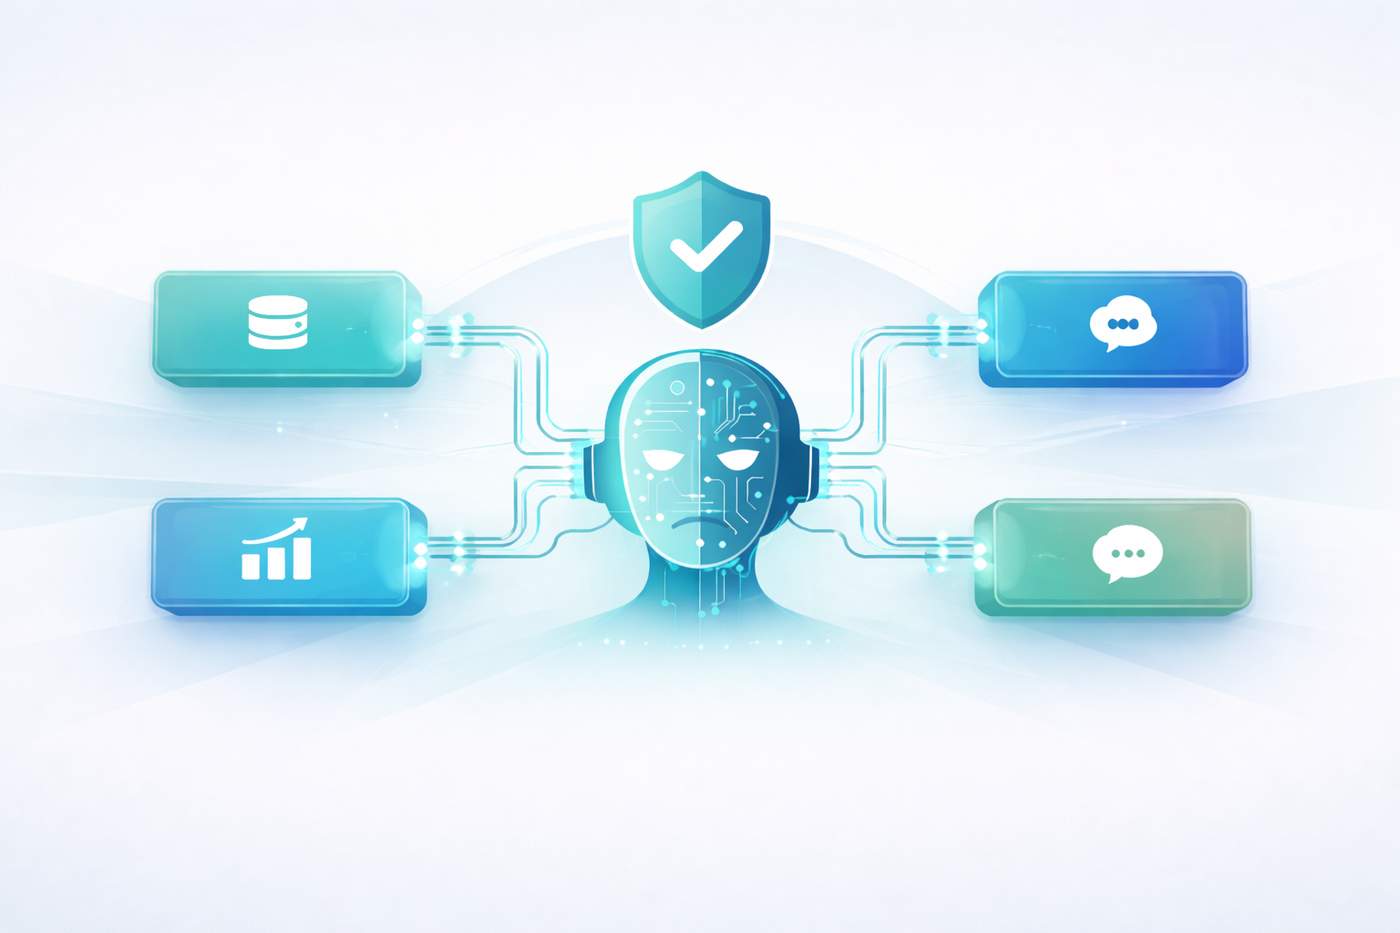
Instead of blind execution, ProWorkBench introduces an approval boundary:
Agent analyzes the task
Agent proposes actions
User explicitly approves execution
Action runs with visibility and audit trace
This small shift changes the trust model entirely.
It allows agents to remain powerful while keeping humans in the loop for risky operations.
Governance as an Engineering Feature
Governance is often treated as a compliance problem. I think it is an engineering problem.
If agents are going to operate inside real environments, they need:
Explicit execution boundaries
Policy controls
Visibility into proposed actions
Clear separation between planning and execution
ProWorkBench treats governance as a first‑class architectural decision rather than an afterthought.
Plugins Instead of a Monolith
Another design decision was extensibility.
Rather than hard‑coding every feature into the core agent runtime, ProWorkBench uses a plugin system. This allows capabilities to evolve independently:
Writing tools
Automation workflows
Integrations
Enterprise extensions (planned)
This keeps the core stable while allowing experimentation at the edges.
Why Build This Now?
AI agents are moving from novelty to infrastructure.
The next wave of systems won’t just be “more autonomous.” They’ll need to be:
Observable
Auditable
Policy‑aware
Operationally safe
My hypothesis is simple:
The winning agent platforms won’t be the most autonomous — they’ll be the most trustworthy.
What’s Next
The long‑term direction for ProWorkBench is an ecosystem approach:
PB Surface — operational interface layer
PB Worker — distributed execution nodes
PB Workstation — enterprise deployment model
All built around governed autonomy rather than unrestricted execution.
Looking for Feedback
If you’re building agents, I’d genuinely love to hear:
Where do you draw the line between autonomy and control?
Should agents ever execute without approval?
What governance mechanisms actually work in practice?
Project: https://proworkbench.com
Code: https://github.com/jamiegrl100/proworkbench/
I’m building this publicly and iterating based on real usage, so honest feedback — especially critical feedback — is welcome.

Comment